Table of Contents
The NIMC Act 2026 penalties for businesses now include corporate fines of up to ₦20 million and personal criminal liability for executives, covering offenses such as unauthorized access to identity data, multiple registration, and identity fraud. If your business collects, stores, or verifies National Identification Numbers in any way, this new law changes what “compliance” means for you, starting now.
That single sentence should make every compliance officer in Nigeria sit up. For almost twenty years, the old NIMC Act of 2007 barely mentioned private companies at all. It was written for a paper-based world, long before banks, telcos, fintechs, and insurers began relying on the National Identification Number, NIN, as a daily verification tool. That gap has now closed, and it closed with teeth.
What Is the NIMC Act 2026? A Quick Recap
On June 26, 2026, President Bola Tinubu signed the National Identity Management Commission Act 2026 into law, repealing the two-decade-old NIMC Act of 2007. The new law does far more than update a few clauses; it rebuilds Nigeria’s identity framework from the ground up.
Under the Act, the NIN becomes Nigeria’s single, legally recognized means of identification. It also designates NIMC as the Root Certification Authority for the country’s National Public Key Infrastructure and Digital Public Infrastructure, placing the Commission at the centre of digital signatures, encrypted transactions, and identity verification nationwide.
For businesses, the practical effect is simple: if your onboarding process, KYC checks, HR records, or customer database touches NIN-linked data in any form, you are now operating inside a regulated space with real consequences for getting it wrong.
Why NIMC Act 2026 Penalties for Businesses Matter Right Now
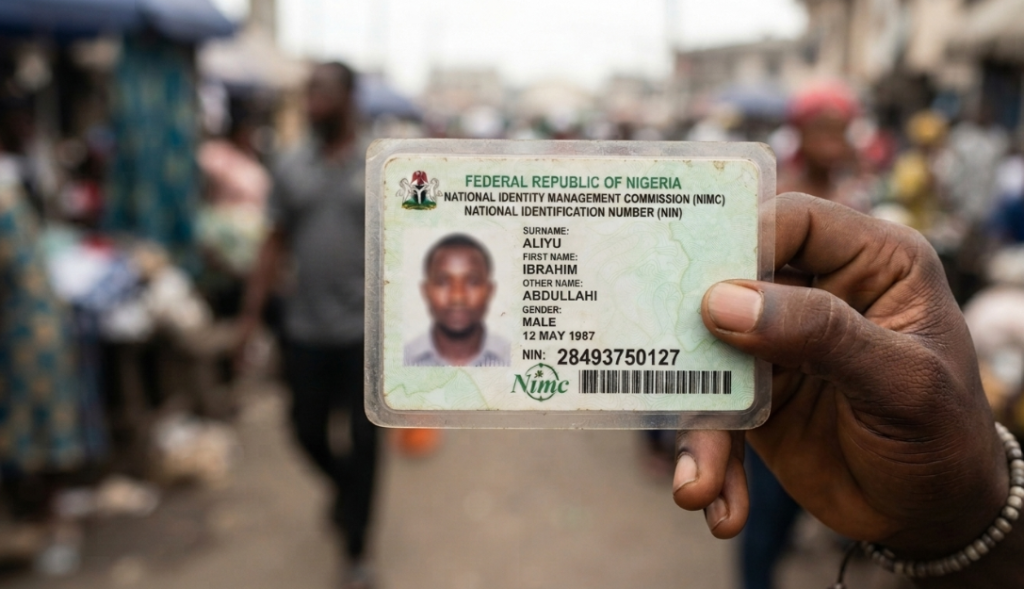
Many Nigerian companies still treat identity data casually. HR departments photocopy NIN slips and store them in unsecured folders. Fintech platforms retain verification data long after a transaction closes. Enrollment agents sometimes cut corners to hit registration targets.
Under the old regime, this carelessness rarely had serious legal consequences. Under the NIMC Act 2026, it does. The law was written specifically because Nigeria’s Minister of Interior and NIMC’s leadership have flagged rising cases of identity theft, multiple registrations, and unauthorized data access as national security concerns, not just administrative nuisances.
This is precisely why understanding NIMC Act 2026 penalties for businesses is no longer optional reading for legal and compliance teams. It is a direct input into how your company should design its data handling processes going forward.
The Specific Offences That Trigger Penalties
The Act does not leave much room for guessing what counts as a violation. The offenses that attract sanctions include the following:
- Unauthorised access to identity information held in the National Identity Database
- Multiple registration or attempts to obtain more than one NIN
- Impersonation, or presenting another person’s identity as your own
- Improper handling, sharing, or exposure of NIN-linked personal data
- Operating an enrolment centre or verification process without proper authorisation
Notice that several of these offenses are things a business can commit indirectly, not just something an individual fraudster does. A company that fails to secure its database, or that shares customer identity data with a third party without consent, can fall squarely into this net.
How Much Are the New Fines? A Clear Breakdown
Here is where the NIMC Act 2026 penalties for businesses become concrete. Corporate organizations found guilty of violations face fines of up to ₦20 million. That figure alone represents an increase the government has described as roughly one hundred times higher than penalties under the old 2007 Act.
For individuals, the law prescribes a minimum of five years’ imprisonment for offenses such as unauthorized access, multiple registration, and impersonation, alongside fines that, in some interpretations of the Act, start from ₦10 million. These are not suggested guidelines; they are statutory minimums.
It is worth pausing on that distinction. A “minimum” of five years means courts have little room to hand down a lighter sentence once guilt is established. That should change how risk-averse your compliance policy needs to be.
Beyond Fines: Criminal Liability for Executives
Perhaps the most underappreciated part of these corporate penalties is that liability does not stop at the company’s door. Reports on the Act indicate that responsible executives and directors may face personal criminal liability where a corporate breach occurs under their watch.
This mirrors a broader trend in Nigerian regulatory law, seen already in areas like data protection and anti-money laundering compliance, where regulators increasingly hold named individuals accountable rather than allowing a company to absorb blame as an abstract entity.
If you sit on a board, run a compliance function, or head an HR department that manages NIN records, this is your signal to treat identity data governance as a personal responsibility, not just a company policy document sitting in a shared drive.

NIMC’s New Enforcement Powers
The 2007 Act gave NIMC mostly administrative functions. The 2026 Act is different. It grants the Commission court-authorized investigative powers, including the ability to conduct searches, seize evidence, decrypt data, and make arrests in connection with identity-related offenses.
In practical terms, NIMC can now act more like a law enforcement partner than a passive record-keeper. The Commission has already signaled intent to intensify audits of enrollment partners and third-party integrators, meaning businesses that rely on external vendors for identity verification should not assume that outsourcing removes their own exposure.
This enforcement shift is a major reason these compliance risks deserve board-level attention rather than being filed away as a legal team’s problem alone.
Which Businesses Are Most at Risk?
Not every company faces the same level of exposure, but the list of affected sectors is broader than many owners assume:
- Banks and fintechs that run NIN-based KYC and onboarding
- Telecom operators managing SIM registration tied to NIN
- Insurance companies processing claims that require identity verification
- HR and recruitment firms that collect NIN slips during hiring
- NIMC enrolment agents and licensed partners
- Any business integrating third-party identity verification APIs into its platform
If your company falls into any of these categories or works with vendors who do, the NIMC Act 2026 penalties for businesses are not a hypothetical risk sitting in a future compliance calendar. They apply to decisions your team is making this week.
7 Practical Steps to Stay Compliant and Avoid Penalties
Understanding the law is only half the job. Here is a working checklist to reduce your exposure:
- Audit where NIN data lives. Map every system, spreadsheet, and vendor that touches identity information across your business.
- Limit access strictly. Only staff who genuinely need NIN data for their role should be able to view or export it.
- Get explicit consent. Under the Act’s alignment with the Nigeria Data Protection Act, consent is not optional; document it properly.
- Vet your enrollment partners. If you use third-party verification providers, confirm they are properly licensed and audited.
- Train your HR and onboarding teams. Most breaches happen through human error, not sophisticated hacking.
- Set a data retention policy. Do not keep NIN-linked records longer than necessary for the purpose collected.
- Review your compliance policy regularly. As NIMC issues implementation guidelines, update your internal procedures to match.
None of these steps require a large legal budget. They require discipline and a clear understanding of what the law now expects.

How the Act Aligns With Data Protection Law
One detail that often gets lost in the headlines about fines is that the NIMC Act 2026 does not stand alone. It was deliberately written to work alongside the Nigeria Data Protection Act, NDPA, which already governs how personal data must be collected, processed, and stored across all sectors.
This matters for businesses because it means you could face exposure under two overlapping regimes at once. A single data mishandling incident involving NIN records could trigger scrutiny from both NIMC and the Nigeria Data Protection Commission, depending on how the breach occurred and who was affected.
The practical takeaway is that your compliance strategy should not treat “NIN handling” and “general data protection” as separate boxes to tick. They now sit under one umbrella, and regulators are likely to look at both when investigating a complaint.
What Implementation Will Look Like Over the Coming Months
Laws of this scale rarely take full effect overnight, and the NIMC Act 2026 is no exception. NIMC’s leadership has already indicated it will roll out implementation guidelines, intensify audits of enrollment partners, and expand its storage and verification infrastructure in phases.
For businesses, this creates a narrow but real window. Companies that use this period to review their data practices, retrain staff, and tighten vendor contracts will be in a far stronger position than those who wait for an actual enforcement action to force the issue.
It is also worth watching for sector-specific guidance. Banking, telecoms, and insurance regulators may issue their own circulars interpreting how these penalties apply within their industries, similar to how the Central Bank of Nigeria has historically issued guidance following major federal legislation.
How to Verify the Full Legal Text
Because the NIMC Act 2026 penalties for businesses carry such serious consequences, it is worth reading the actual statutory language rather than relying only on summaries. You can access the full National Identity Management Commission (Establishment) Act, 2026 directly through Lexark’s legal document library, where the complete Act is searchable alongside related Nigerian laws and regulations.
For businesses that also handle government contracts or procurement, it is worth noting that Nigeria’s tender ecosystem is worth an estimated ₦10 trillion annually, and identity verification is increasingly becoming part of the bidding process itself, another reason to get your NIN compliance house in order early.
If you want a broader view of how this legislation affects day-to-day operations beyond penalties, our earlier piece on NIMC Act 2026 compliance for businesses breaks down the operational side in more depth, while our explainer on the changes covers the wider reform for readers who are new to the topic.
What is the maximum fine for a company under the NIMC Act 2026?
Corporate organizations found guilty of violations such as unauthorized access or data mishandling face fines of up to ₦20 million.
Can company executives be held personally liable?
Yes. Reports on the Act indicate that responsible officers can face personal criminal liability alongside corporate fines, depending on the nature and severity of the breach.
Does the Act apply to businesses that outsource identity verification?
Yes. Using a third-party vendor does not remove your company’s responsibility; NIMC has signaled it will intensify audits of enrollment partners and integrators.
Where can I read the full text of the Act?
The complete NIMC Act 2026 is available through Lexark’s legal database, alongside AI-assisted search across other Nigerian laws and regulations.
Conclusion
The government has been explicit about its intentions here. President Tinubu himself warned that penalties for identity-related offences have been increased “by up to 100 times,” a phrase that should tell you everything about how seriously this administration intends to enforce the new rules.
For a Nigerian business, ignoring the NIMC Act 2026 penalties for businesses is no longer a quiet compliance gap you can fix later; it is an active legal and financial exposure sitting inside your customer database right now. So the real question is not whether your company will eventually have to comply, but whether you will get ahead of it before an audit finds the gaps for you.