Table of Contents
NIMC Act 2026 compliance for businesses means one simple thing: any Nigerian company that collects, stores, verifies, or processes identity data linked to a National Identification Number (NIN) is now legally bound by stricter data protection rules and much heavier penalties for getting it wrong. Below, we break down exactly what changed and the six steps businesses should take immediately.
What the NIMC Act 2026 Changed for Businesses
On June 26, 2026, President Bola Tinubu signed the NIMC Act 2026 into law, replacing a framework that had stood unchanged since 2007. For most Nigerians, the headline news was about national identity cards and passports. For businesses, the real story is quieter but far more consequential: the Act rewrites the legal obligations of any organisation that touches NIN-linked data.
The National Identity Management Commission (NIMC) has been designated as Nigeria’s Root Certification Authority for the National Public Key Infrastructure (PKI) and Digital Public Infrastructure (DPI). In practice, this places NIMC at the centre of digital trust for the entire country, and it means every business that relies on identity verification, from banks to telecom providers to fintech startups, now operates inside a much stricter regulatory perimeter.
The Act also formally aligns identity data handling with the Nigeria Data Protection Act (NDPA), closing a long-standing gap where identity law and privacy law did not fully speak to each other.
Why This Matters Right Now

Here is the part that should get every compliance officer’s attention. Under the NIMC Act 2026, penalties for identity-related offences have increased by as much as 100 times compared to the old law. Corporate bodies found guilty of mishandling identity data can now face fines of up to ₦20 million. Individuals responsible for unauthorised access, multiple registration, or impersonation face a minimum of five years’ imprisonment.
The law also grants NIMC court-authorised powers to investigate offences, conduct searches, seize evidence, decrypt data, and arrest suspects connected to identity-related crimes. This is not a symbolic update. It is enforcement infrastructure with real teeth, and it applies to private-sector organisations just as much as government agencies.
For businesses, waiting to “see how enforcement plays out” is a risky strategy. Regulators in Nigeria have shown, through the Nigeria Data Protection Commission’s enforcement actions in recent years, that fines and investigations do materialise once a legal framework is in place.
Who Is Directly Affected
NIMC Act 2026 compliance for businesses is not limited to the obvious players like banks and telecom companies. It affects any organisation that:
- Verifies customer identity using NIN as part of onboarding, such as fintech apps, insurers, and lending platforms.
- Stores biometric or identity-linked data on employees or customers, including HR departments and payroll providers.
- Integrates with NIMC’s verification infrastructure through APIs or third-party identity checks.
- Operates in regulated sectors such as banking, oil and gas, or telecoms, where identity verification is already a licensing requirement.
- Handles government tenders or contracts that require verified business ownership and beneficial ownership disclosure.
If your business falls into any of these categories, the NIMC Act 2026 is not background news. It is a direct compliance obligation.
6 Urgent Steps for NIMC Act 2026 Compliance for Businesses

1. Audit How Your Business Collects and Stores Identity Data
Start with a simple internal audit. Map out every point where your business collects a customer’s or employee’s NIN, biometric data, or other identity information. Many companies are surprised to discover just how many departments, vendors, or third-party tools touch this data without a formal review process.
2. Align Your Data Protection Policy With the NDPA
Since the NIMC Act 2026 explicitly ties identity data handling to the Nigeria Data Protection Act, your internal data protection policy needs to reflect NDPA principles: lawful basis for processing, purpose limitation, and clear consent mechanisms. If your current policy predates 2023, it is almost certainly out of date.
3. Review Third-Party and Vendor Integrations
If your business uses external vendors for identity verification, KYC checks, or onboarding, confirm that those vendors are themselves compliant. Liability does not disappear just because a third party handled the actual data processing; regulators typically expect the primary business to have done its due diligence.
4. Train Staff on the New Penalty Structure
Employees handling identity data need to understand that the cost of mistakes has changed dramatically. A five-year minimum prison term for unauthorised access is not an abstract legal detail; it is a reason to tighten internal access controls, permissions, and audit trails around who can view or export identity records.
5. Update Consent Language in Customer-Facing Materials
Review your terms of service, onboarding forms, and privacy notices to make sure consent language is explicit about how NIN-linked data will be used, stored, and shared. Vague or bundled consent clauses are increasingly risky under a framework built around purpose limitation.
6. Build a Relationship With Legal Counsel Who Track Regulatory Change
Perhaps the most overlooked step is also the simplest: regulatory frameworks like the NIMC Act 2026 do not stay static. Implementation guidelines, secondary regulations, and enforcement priorities will continue to evolve. Businesses that treat compliance as a one-time project, rather than an ongoing relationship with legal and regulatory monitoring, tend to fall behind. This is exactly the kind of fast-moving regulatory landscape where a searchable Nigerian legal regulations database becomes genuinely useful, since it lets your team track amendments and related statutes in one place instead of relying on scattered news coverage.
Sector-Specific Implications
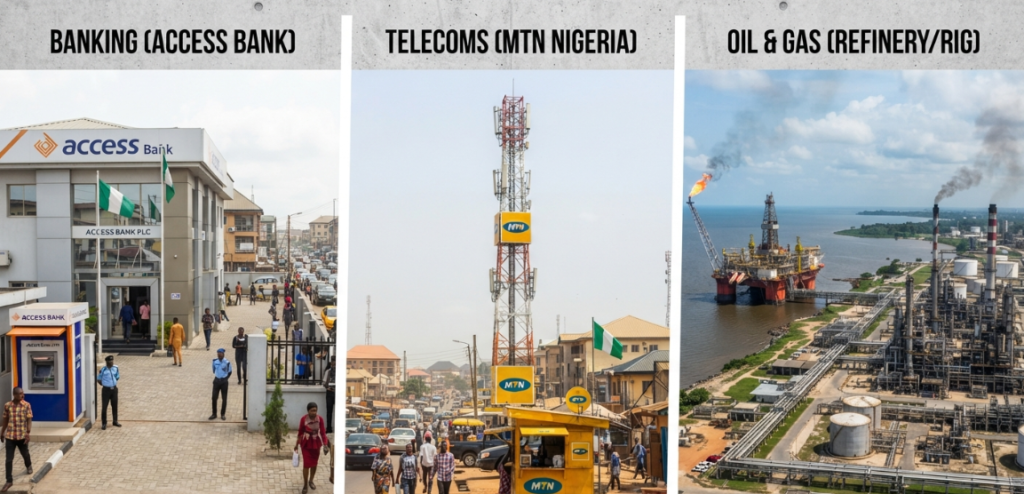
Different industries will feel this law differently. Banks and other financial institutions, already accustomed to strict Know Your Customer (KYC) obligations from the Central Bank of Nigeria, will likely see the NIMC Act 2026 as reinforcing existing practice rather than upending it, though penalty exposure is now considerably higher.
Telecom providers, who have handled NIN-linked SIM registration for years, face similar reinforcement, with added pressure to ensure their identity verification pipelines meet the new PKI and DPI standards NIMC now oversees.
Oil and gas companies, along with other heavily regulated industries, may feel the impact indirectly through contractor and vendor onboarding, particularly where government tenders require verified business ownership.
NGOs and consultants who regularly bid for government contracts should also pay attention, since verified identity and beneficial ownership disclosure increasingly intersect with Nigeria’s procurement processes. Businesses navigating that tender landscape alongside new identity compliance requirements often benefit from tools that consolidate both regulatory search and procurement opportunity tracking in a single workspace, which is part of why platforms built for Nigeria’s legal and business environment continue to gain traction.
Common Compliance Mistakes to Avoid
Many businesses will get this wrong in predictable ways. The most common mistake is treating identity compliance as purely an IT problem, when it is actually a cross-functional issue involving legal, HR, customer service, and vendor management.
A second common mistake is assuming that because a business “isn’t a bank,” it is not exposed. Any company that stores employee NIN records for payroll purposes is already handling regulated data.
A third mistake is delaying policy updates until formal implementation guidelines are published. Given how quickly Nigerian regulators have moved on related frameworks, businesses that wait for every technical detail before acting often find themselves playing catch-up.
What Happens If a Business Fails to Comply
It helps to walk through what non-compliance actually looks like in practice, rather than treating it as an abstract risk. Picture a mid-sized fintech that stores customer NIN records for onboarding but never updated its consent language or access controls after 2023. If that company suffers a data breach, or if an employee is caught exporting identity records without authorisation, the business is now exposed on two fronts at once: potential NDPA enforcement action for the privacy failure, and NIMC Act 2026 penalties for the identity-data mishandling itself.
That double exposure is precisely why NIMC Act 2026 compliance for businesses cannot be treated as a box-ticking exercise handled entirely by IT. A breach investigation typically triggers scrutiny of governance, not just technical controls; regulators tend to ask who approved the data handling process, whether staff were trained, and whether the business had a documented policy at all. Companies that can produce clear answers to those questions, backed by an audit trail, are in a materially stronger position than those that cannot.
There is also a reputational dimension that is easy to underestimate. Nigerian consumers and business partners are increasingly aware of identity theft risks, partly because of how visible cases like SIM swap fraud and NIN-linked scams have become in the media. A publicised compliance failure does not just carry a fine; it can quietly erode customer trust in ways that are much harder to repair than the financial penalty itself.
The upside is that compliance, once properly built into a company’s operations, does not need to be revisited constantly. A well-structured data protection policy, clear consent flows, and a documented vendor review process create a foundation that scales with the business rather than becoming a recurring emergency every time a regulator issues new guidance.
The Role of Legal and Compliance Teams
In-house legal departments and external counsel both have a role to play here. In-house teams are best positioned to audit internal data flows and train staff, while external counsel can provide interpretation on ambiguous provisions and represent the business if a dispute or investigation arises.
For law firms advising clients through this transition, efficient legal research matters more than ever. Nigerian legal professionals increasingly rely on AI-assisted legal research tools to keep pace with fast-moving regulatory changes like this one, cutting down the hours once spent manually cross-referencing statutes and regulations. Firms that pair this kind of research efficiency with strong litigation and practice management habits tend to advise clients with more confidence during periods of regulatory transition.
What is NIMC Act 2026 compliance for businesses in simple terms?
It refers to the legal obligations businesses now carry under the new law, including stricter data protection standards and steep penalties for mishandling identity data linked to a customer’s or employee’s NIN.
What is the maximum fine for a business under the NIMC Act 2026?
Corporate bodies found guilty of violations, such as mishandling or breaching identity data, can face fines of up to ₦20 million.
Do small businesses need to worry about NIMC Act 2026 compliance?
Yes, if they collect, store, or process NIN-linked data in any form, including payroll records or customer onboarding, regardless of company size.
Does the NIMC Act 2026 require businesses to update their privacy policies?
While the Act does not list this as a specific line item, its alignment with the Nigeria Data Protection Act makes updated, consent-based privacy policies a practical necessity for compliant businesses.
Regulatory deadlines rarely announce themselves twice; the businesses that treat NIMC Act 2026 compliance as urgent today are the ones that will not be scrambling to explain a data breach to regulators tomorrow.